
The Developer’s Guide to Debugging AI-Generated Code
To debug AI-generated API code, reproduce the failing request, compare the actual response with the required behavior, make a targeted fix, and run the same check again. Preserve a recording of working behavior before changing an existing service.
Speedscale’s proxymock CLI and Model Context Protocol (MCP) server let your coding assistant record requests, mock dependencies, and replay traffic against a candidate. The request and response differences give you evidence to inspect alongside the code diff. Keep unit tests and security checks for requirements the recording doesn’t cover.
Start with the existing Cursor recording and replay walkthrough for a local example. Once you have a repeatable check, use the verified AI-code CI/CD tutorial to make regressions fail the job. This guide covers how to diagnose the failure between those steps.
Choose the check that fits the failure
A green build only answers part of the question. First identify what failed and what evidence would distinguish an application bug from a test setup problem.
| Symptom | Start here | Evidence to inspect |
|---|---|---|
| App won’t compile or start | Compiler, type checker, installed package versions, official API docs | Exact error and the smallest failing call |
| API returns the wrong value | Reproduce the request; compare a replay against the reviewed baseline | Status, response body, dependency calls, candidate revision |
| Replay gets a 401 or 403 | Check credentials and token correlation before changing business logic | Which token each request sends and which response produced it |
| App slows under load | Profile it; run a separate controlled performance test | Workload, dependency behavior, latency and resource use |
| Authentication or input handling looks unsafe | Targeted security review and configured security tools | Requirement, reachable code path, finding and test case |
For an incorrect result, write down the expected behavior independently of the candidate. If you let the agent derive both the implementation and every expected answer from the same assumption, both can agree on the same mistake.
Connect the coding assistant to proxymock
Install and activate proxymock using the installation instructions. Reuse an existing valid account configuration. Then check your installed version and configure the MCP client:
proxymock version --client
proxymock mcp install
The installer detects supported clients and prompts interactively. proxymock mcp install --yes installs into every detected client, so use it only when that is what you intend. Run proxymock mcp install --help to see the options your version supports. Reload the client if needed and confirm that proxymock’s tools appear in its tool list before asking it to record anything.
These instructions were last checked against proxymock v2.5.1309 on November 3, 2026, including a local stdio handshake and the server’s live tool registry. Stdio is the default transport: the client launches the proxymock process. You do not need to start a separate HTTP server for that setup. See the MCP setup reference.
LLM prompt for this step
Install and activate proxymock using its installation instructions, reusing my existing valid account configuration if there is one, and report `proxymock version --client`. Then run `proxymock mcp install` to register proxymock's MCP server with my coding agent using its supported setup. It prompts interactively; do not pass `--yes` unless I confirm I want it installed into every detected client. Check `proxymock mcp install --help` for the options my version supports before adapting the command. Use the default stdio transport and do not start a separate HTTP server. Reload my coding agent if needed and confirm proxymock's tools appear in its tool list before recording anything. Report the version, the commands you ran, the tools you saw, and anything you could not verify.Keep the server in the application directory
The examples in this guide use the Go app in mock-lab, Speedscale’s sample repository. Run recording and replay from its languages/go directory. A repository can contain several apps; avoid recording from a directory containing unrelated workspace files.
For manual configuration, follow your client’s schema. VS Code uses servers in .vscode/mcp.json; Cursor and some other clients use mcpServers. The installer handles that difference. For example, this VS Code entry pins the server’s working directory to the existing Go app. Replace both absolute paths:
{
  "servers": {
    "proxymock": {
      "type": "stdio",
      "command": "/absolute/path/to/proxymock",
      "args": [
        "mcp", "run", "--work-dir",
        "/absolute/path/to/mock-lab/languages/go"
      ]
    }
  }
}
Follow VS Code’s MCP configuration instructions for trust and tool controls. An assistant can inspect files, fetch documentation, or run commands only when the relevant tools and permissions are available. Check its tool output rather than assuming it verified a library signature or executed a test.
LLM prompt for this step
Check my proxymock version and configure its MCP integration for the actual application directory. Use the assistant's supported configuration schema, resolve the binary path and work directory, and verify the available tools.Preserve the recording and the baseline replay
The existing walkthrough uses the same mock-lab Go app. Its recording includes project queries and an authenticated order flow, with a blueprint that carries fresh tokens and order IDs into later requests.
Keep two artifacts distinct:
- The source recording supplies the inbound requests and recorded dependency responses. Keep it unchanged while investigating a candidate.
- The baseline replay output records how known-good code responded to those requests. The MCP
baselineparameter takes this replay output directory, not the raw source recording.
Review the known-good responses against your requirements before accepting them. A recording can preserve an existing bug. For intentional behavior changes, add requirement-driven tests and review fixture updates separately.
The MCP tools reference describes the current parameters. The names used in the earlier IDE example remain available: record_traffic_start, mock_server_start, and replay_traffic. A started replay is asynchronous. Use list_running and read_process_logs to follow it to completion, then inspect its output directory, verdict, and process result.
Make dependency isolation explicit
In the checked version, mock_server_start does not expose the CLI’s --no-passthrough option. Check the tool’s parameters in your client before relying on it. Do not assume that starting an MCP mock server prevents unmatched requests from reaching real dependencies.
When you need that behavior for the existing Go example, have the agent use its terminal to start the application through the CLI from languages/go:
proxymock mock --in ./proxymock/recording --no-passthrough -- go run .Unmatched requests that reach this proxy receive an error instead of being forwarded. This does not block connections that bypass the proxy. Confirm your application’s proxy and TLS configuration using the language reference. The CI tutorial supplies the complete readiness, cleanup, replay, and artifact script.
LLM prompt for this step
Run the local Go app using the explicit proxymock/recording dependency set and passthrough disabled. Verify required calls match the fixture and surface missing recordings as failures before attempting a code fix.Give the agent a debugging task with evidence
Use an instruction that fixes the comparison boundary and asks for the failing request, rather than another broad rewrite:
Reproduce the failing API behavior using the saved source recording.
Keep that recording and the reviewed baseline replay unchanged.
Start the app with `proxymock mock --no-passthrough` from the terminal,
not the MCP mock tool, so unmatched proxied calls fail instead of passing through.
Compare the candidate against the baseline replay and wait for completion.
Report each changed status or stable body value, the observed response,
the replay output directory, configuration, verdict, and process exit code.
Distinguish token/ID correlation failures from application regressions.
Make a targeted code fix, then rerun the same comparison and report its result.
For MCP replay, explicitly set baseline to the reviewed replay output and fail-on-new-mismatch to true. The equivalent CLI gate is --baseline <replay-output> --fail-on-new-mismatch. A new per-request regression exits 3; other nonzero results can indicate failed goals or operational errors. See the replay verdict reference.
A completed request with HTTP 200 can still have the wrong body. A replay finishing, or an assistant saying it fixed the code, is not evidence that the comparison passed. Keep the verdict and observed responses with the candidate revision so another engineer can inspect them.
Inspect the difference before changing the code
The controlled example in the existing CI tutorial changes mock-lab’s project count from 24 to 25. All eight recorded requests still complete, and /api/stats still returns HTTP 200. The gate finds one new stable-body mismatch and exits 3. Restoring the calculation makes the same comparison pass again.
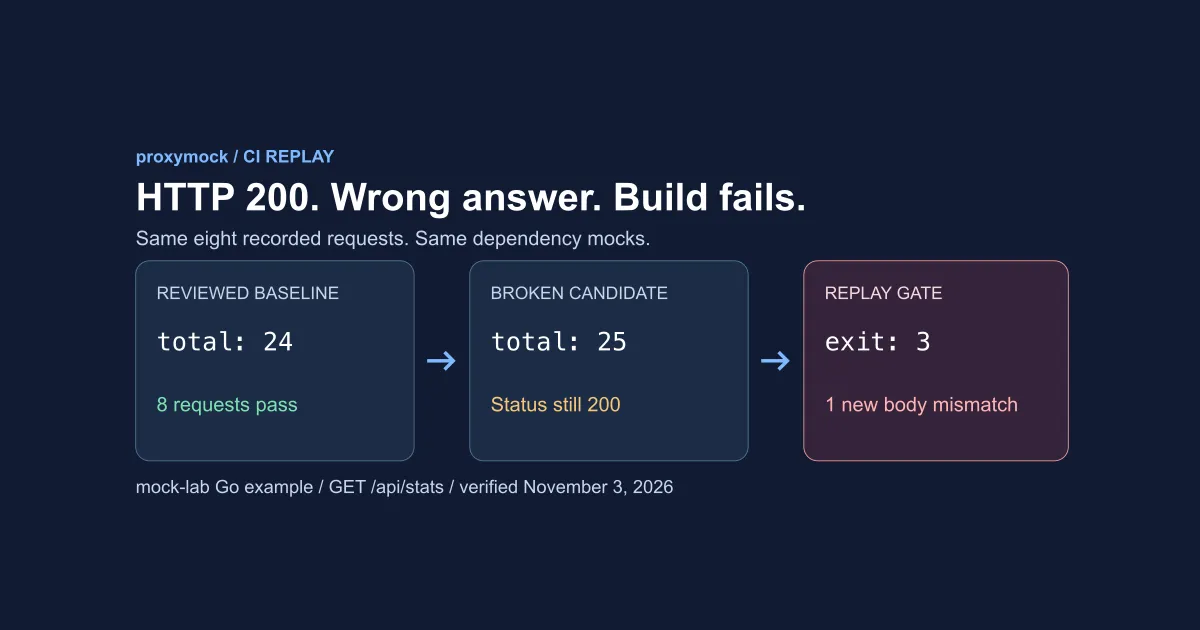
That result identifies a specific calculation to investigate. It does not require recreating the app, recording a new expected answer, or asking the agent to replace unrelated code.
A failed authenticated request can need a different fix. The existing local walkthrough shows stale tokens and order IDs corrected through correlation. Follow the 403 replay guide when the replay sends old values. Changing application authorization to accept a stale token would hide the setup error and weaken the application.
For a missing function or deprecated API, check the actual installed version and its official documentation. Agents with documentation or terminal tools can help verify it, but review what they fetched and ran. Better prompting supplies context; execution and reviewed assertions establish whether the candidate meets the tested requirements.
Keep the fix small and rerun the same checks
Prefer a targeted change when the request difference points to one handler, calculation, or dependency call. Step through that path with a debugger or add a requirement-based test for the failure. If several attempted fixes don’t explain the result, stop and inspect the requests, responses, logs, and assumptions before asking for another rewrite.
A broader rewrite needs a clear requirement and preserved regression checks for the behavior that must remain. Do not discard the failing test or replace its expected answer simply to make the new implementation pass.
Security needs its own checks. Static analysis can detect configured vulnerability patterns, but its coverage depends on the rules, language, and available context. Keep dependency and secret scanning, targeted runtime tests, and manual review where required; see OWASP’s static-analysis guidance. A passing traffic replay does not establish complete security.
For performance, use a separate workload with controlled dependencies and explicit thresholds. A single functional replay is not evidence of production capacity. The AI code verification overview explains where replay fits alongside these other checks.
Originally published by Matt Tanner in 2025. Updated by the Speedscale team in 2026 to reflect the current proxymock MCP setup and replay workflow.
Run this workflow with an LLM
Give this prompt to a coding assistant with access to your project and this article. Supply environment-specific values it cannot discover.
Whole-workflow LLM prompt
Read https://speedscale.com/blog/the-developers-guide-to-debugging-ai-generated-code/ and inspect my project instructions first. Connect my coding assistant to proxymock in the application directory, reproduce the failing API behavior from the preserved recording, run a candidate with dependency passthrough disabled, and use the existing debugging prompt to compare responses and report the exact fix and validation evidence. Check installed tool help before adapting commands. Report the checks actually run, their results, and anything you could not verify.FAQs about debugging AI-generated code
Why does AI code often include non-existent functions?
A model can produce plausible names that do not belong to the installed library. Check the version, imports, and official API reference. If the assistant has documentation or execution tools, ask it to use them and show the result. Access to those tools does not guarantee that it interpreted the result correctly.
Can I trust AI to write production-level code?
Review and test the candidate against your requirements before deploying it. proxymock can check the API behavior present in a saved recording; keep unit, security, and integration checks for requirements outside that recording. Treat the assistant’s explanation as something to verify against the actual test artifacts.
What’s the best way to verify AI-generated logic?
Use assertions derived from the requirement, tests for edge cases, and code review. For an existing API, replay a reviewed recording against the candidate and inspect status and stable-body differences. The CI tutorial’s wrong-total example shows why successful HTTP requests alone are insufficient.
How can I avoid AI coding hallucinations?
Give the assistant the actual interfaces, versions, constraints, and documentation it needs. Require it to run the relevant checks and report their results. Preserve failures as test cases and rerun them after a fix; adding more instructions to the prompt alone does not prove the code works.